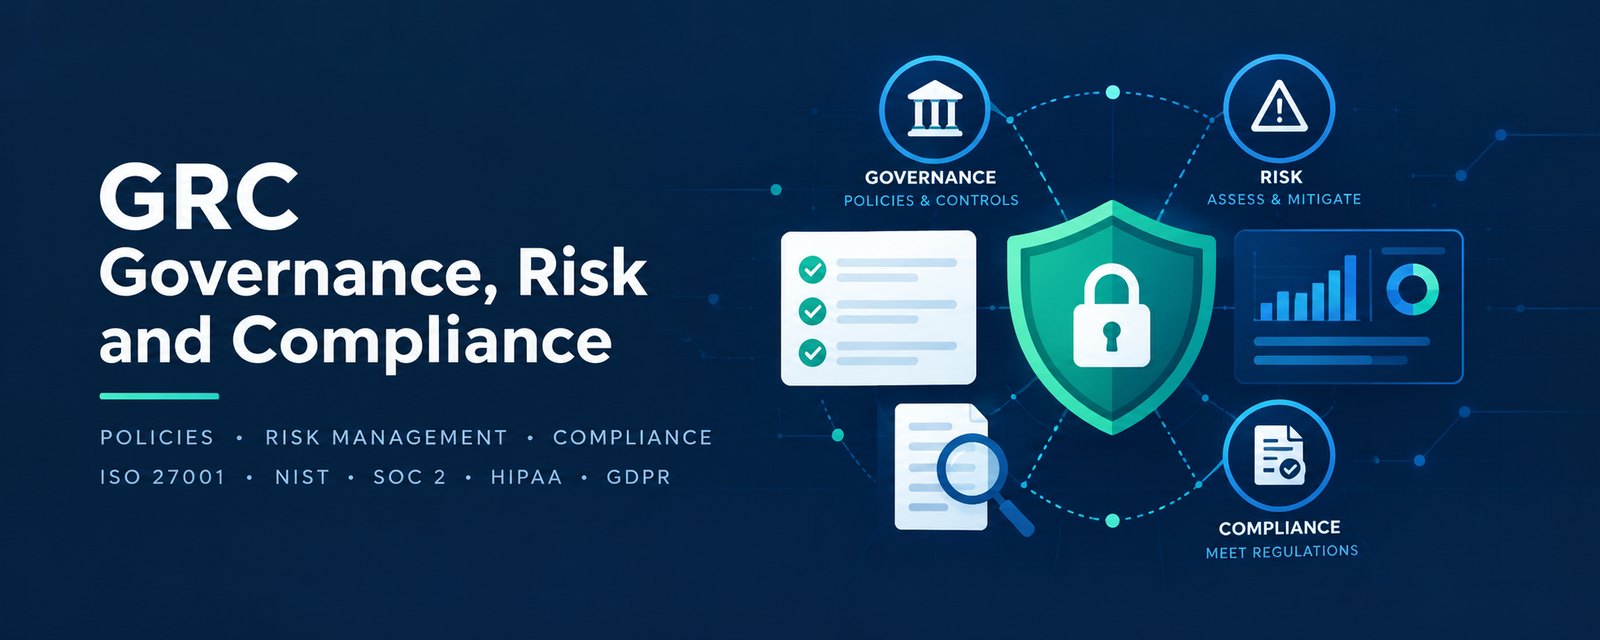
GRC Audit
Incident → Framework diagnostic & remediation
- NIST CSF 2.0
- ISO 27001
- SOC 2
- GDPR
- CCPA/CPRA
- HIPAA
- AIUC-1
Describe any security incident or audit finding in plain language. GRC Audit maps it to NIST CSF 2.0, ISO/IEC 27001:2022, SOC 2, GDPR, CCPA/CPRA, HIPAA and the AIUC-1 AI agent standard — grounded against embedded official catalogs so control IDs are verified, not hallucinated — then lists the audit evidence an assessor will request and builds a 3-step remediation plan.
Companion project · GitHubIdentity Governance Audit FrameworkA full simulated audit engagement: SOC 2 Type 2 integrated with an ISO/IEC 27001 surveillance audit, from risk assessment to control testing workpapers, findings and remediation.(opens on GitHub in a new tab)Built on the GRC lifecycle
Governance, Risk & Compliance isn't a checklist — it's a loop. Every audit this tool runs moves through the same five principles.
Policies, roles and accountability frame every finding and decision.
Classify the incident and map it to controls across seven frameworks.
Rate severity and regulatory exposure; every control ID is grounded.
Contain, investigate & notify, then fix the root cause.
Evidence and continuous controls to detect and prevent recurrence.
Core Principle: The Pillars of Risk Treatment (ISO 31000 & NIST)
Every risk has four possible treatments. The audit below recommends one as its primary strategy — but the others are always on the table.
Implement controls and security baselines to reduce likelihood and impact.
Discontinue the high-risk operational activity entirely.
Reallocate financial or operational liability (cyber insurance, third-party SLAs).
Formally retain the residual risk with documented executive sign-off within corporate risk appetite.
Tip: click a scenario pill above, then “Audit Incident”. Works with zero setup in demo mode; add an API key for full LLM analysis of any incident.
Official sources
Every control ID this tool cites is drawn from, and verified against, the official source for each framework. Paid/copyrighted standards (ISO/IEC 27001, SOC 2) are referenced by official identifier and short title only — the standards' text is not reproduced.
- NIST Cybersecurity Framework 2.0FREE2.0 (February 2024)Official PDF ↓
- ISO/IEC 27001:2022 Annex APAID2022Purchase (paid) ↓
- AICPA SOC 2 — Trust Services CriteriaFREETSC 2017 (revised 2022)Official PDF ↓
- EU General Data Protection Regulation (GDPR)FREERegulation (EU) 2016/679Official PDF ↓
- California Consumer Privacy Act (CCPA) as amended by CPRAFREECal. Civ. Code § 1798.100 et seq. + CCR Title 11 regulationsOfficial text ↓
- HIPAA Security, Privacy & Breach Notification RulesFREE45 CFR Part 164 (Security Rule Subpart C in force; Jan-2025 NPRM still proposed)Official text (eCFR) ↓
- AIUC-1 — AI Agent StandardFREEQ4 2026 release (last updated 15 Oct 2026)Official standard ↓